
Article summary: Dear bosses and technical partners, let’s not talk about the frivolous stuff today, let’s talk about the heart-breaking stuff. Is your core code still running naked? I have been in this industry for decades and have seen too many tragedies: the core engineer resigned early, and the source code in the server was later used.
Dear bosses and technical partners, let’s not talk about the frivolous stuff today, let’s talk about the heart-breaking stuff. Is your core code still running naked? I have been in this business for decades and have seen too many tragedies: core engineers resigned early, and the source code in the server was packed away. ; The code from the outsourcing team has not been accepted yet, and a "high imitation version" has been released on the market.” ; There are even employees who directly drag the SVN warehouse to the mobile hard drive for tens of thousands of dollars. If you think about it, are those millions or tens of millions of R&D investments just "one-pot"? Today I won’t talk to you about those fancy concepts, but I will talk about the territory and how to protect this pile of “lifeblood”.
How to encrypt source code? Summarize 4 ways to encrypt source code, which are super practical and protect source code encryption from being leaked.
1. Deploy the Insight Eye MIT system
 This system is recognized as the "ballast stone" for us old guys who have been working hard for Party A and Party B for so many years. It is not as simple as installing an anti-virus software for you, but directly inserting a "fixing needle" into the kernel layer of the operating system. For code leaks, it plays a real technical flow:
The code is forced to be encrypted without physical isolation. : This is the cruelest move. Regardless of whether you use Visual Studio, IDEA or Notepad, as long as the source code file is written to the disk, it will be encrypted upon landing. This is not the kind of "face-saving project" that only locks the suffix name. Even if you copy the file to a USB flash drive, send it to WeChat, or even remove the hard drive and hang it on another computer, you will see a bunch of garbled characters when you open it. This puts an end to the idea of "physical copies".
Full life cycle audit, precise attack : Who, when, which piece of code was sent out, and through what channel (U disk, Bluetooth, email, network disk)? This system is clearly visible. The "insider" behavior that bosses are most afraid of is the frame-by-frame playback in front of this set of audit logs. Once it is discovered that someone exports sensitive directories in batches, the system will directly intercept and trigger an alarm, and then wipe the butt before the incident occurs.
Outbound control, go out with a "lock" : What should employees do if they have to go on a business trip or coordinate with clients? You can't help but be allowed to bring a computer. This system supports the production of "outbound controllable packages". The code you give can limit the number of times it can be opened, the validity period, and even bind it to a specific machine. Show it to the other party and it will be automatically destroyed when it expires. Want to forward it again? No way.
Sensitive content identification, AI leak prevention : It used to be a “one size fits all” lock, but now it’s smarter. The system can automatically scan the code warehouse to identify whether it contains high-risk information such as database passwords and API keys. If someone tries to write plain text passwords in the code, or mix core algorithm fragments into ordinary documents and send them out, the system will directly judge them as high risk and cut them off immediately.
Screen watermark and print traceability : Don’t underestimate this trick. Regardless of whether you take a photo, screenshot or print, there are watermarks of employee names and job numbers floating on the screen. Even if he really points his phone at the screen and takes a photo, if the photo is leaked, the person responsible can be located in a second based on the watermark. Deterrence is more effective than any punishment.
2. Network isolation and VDI virtual desktop
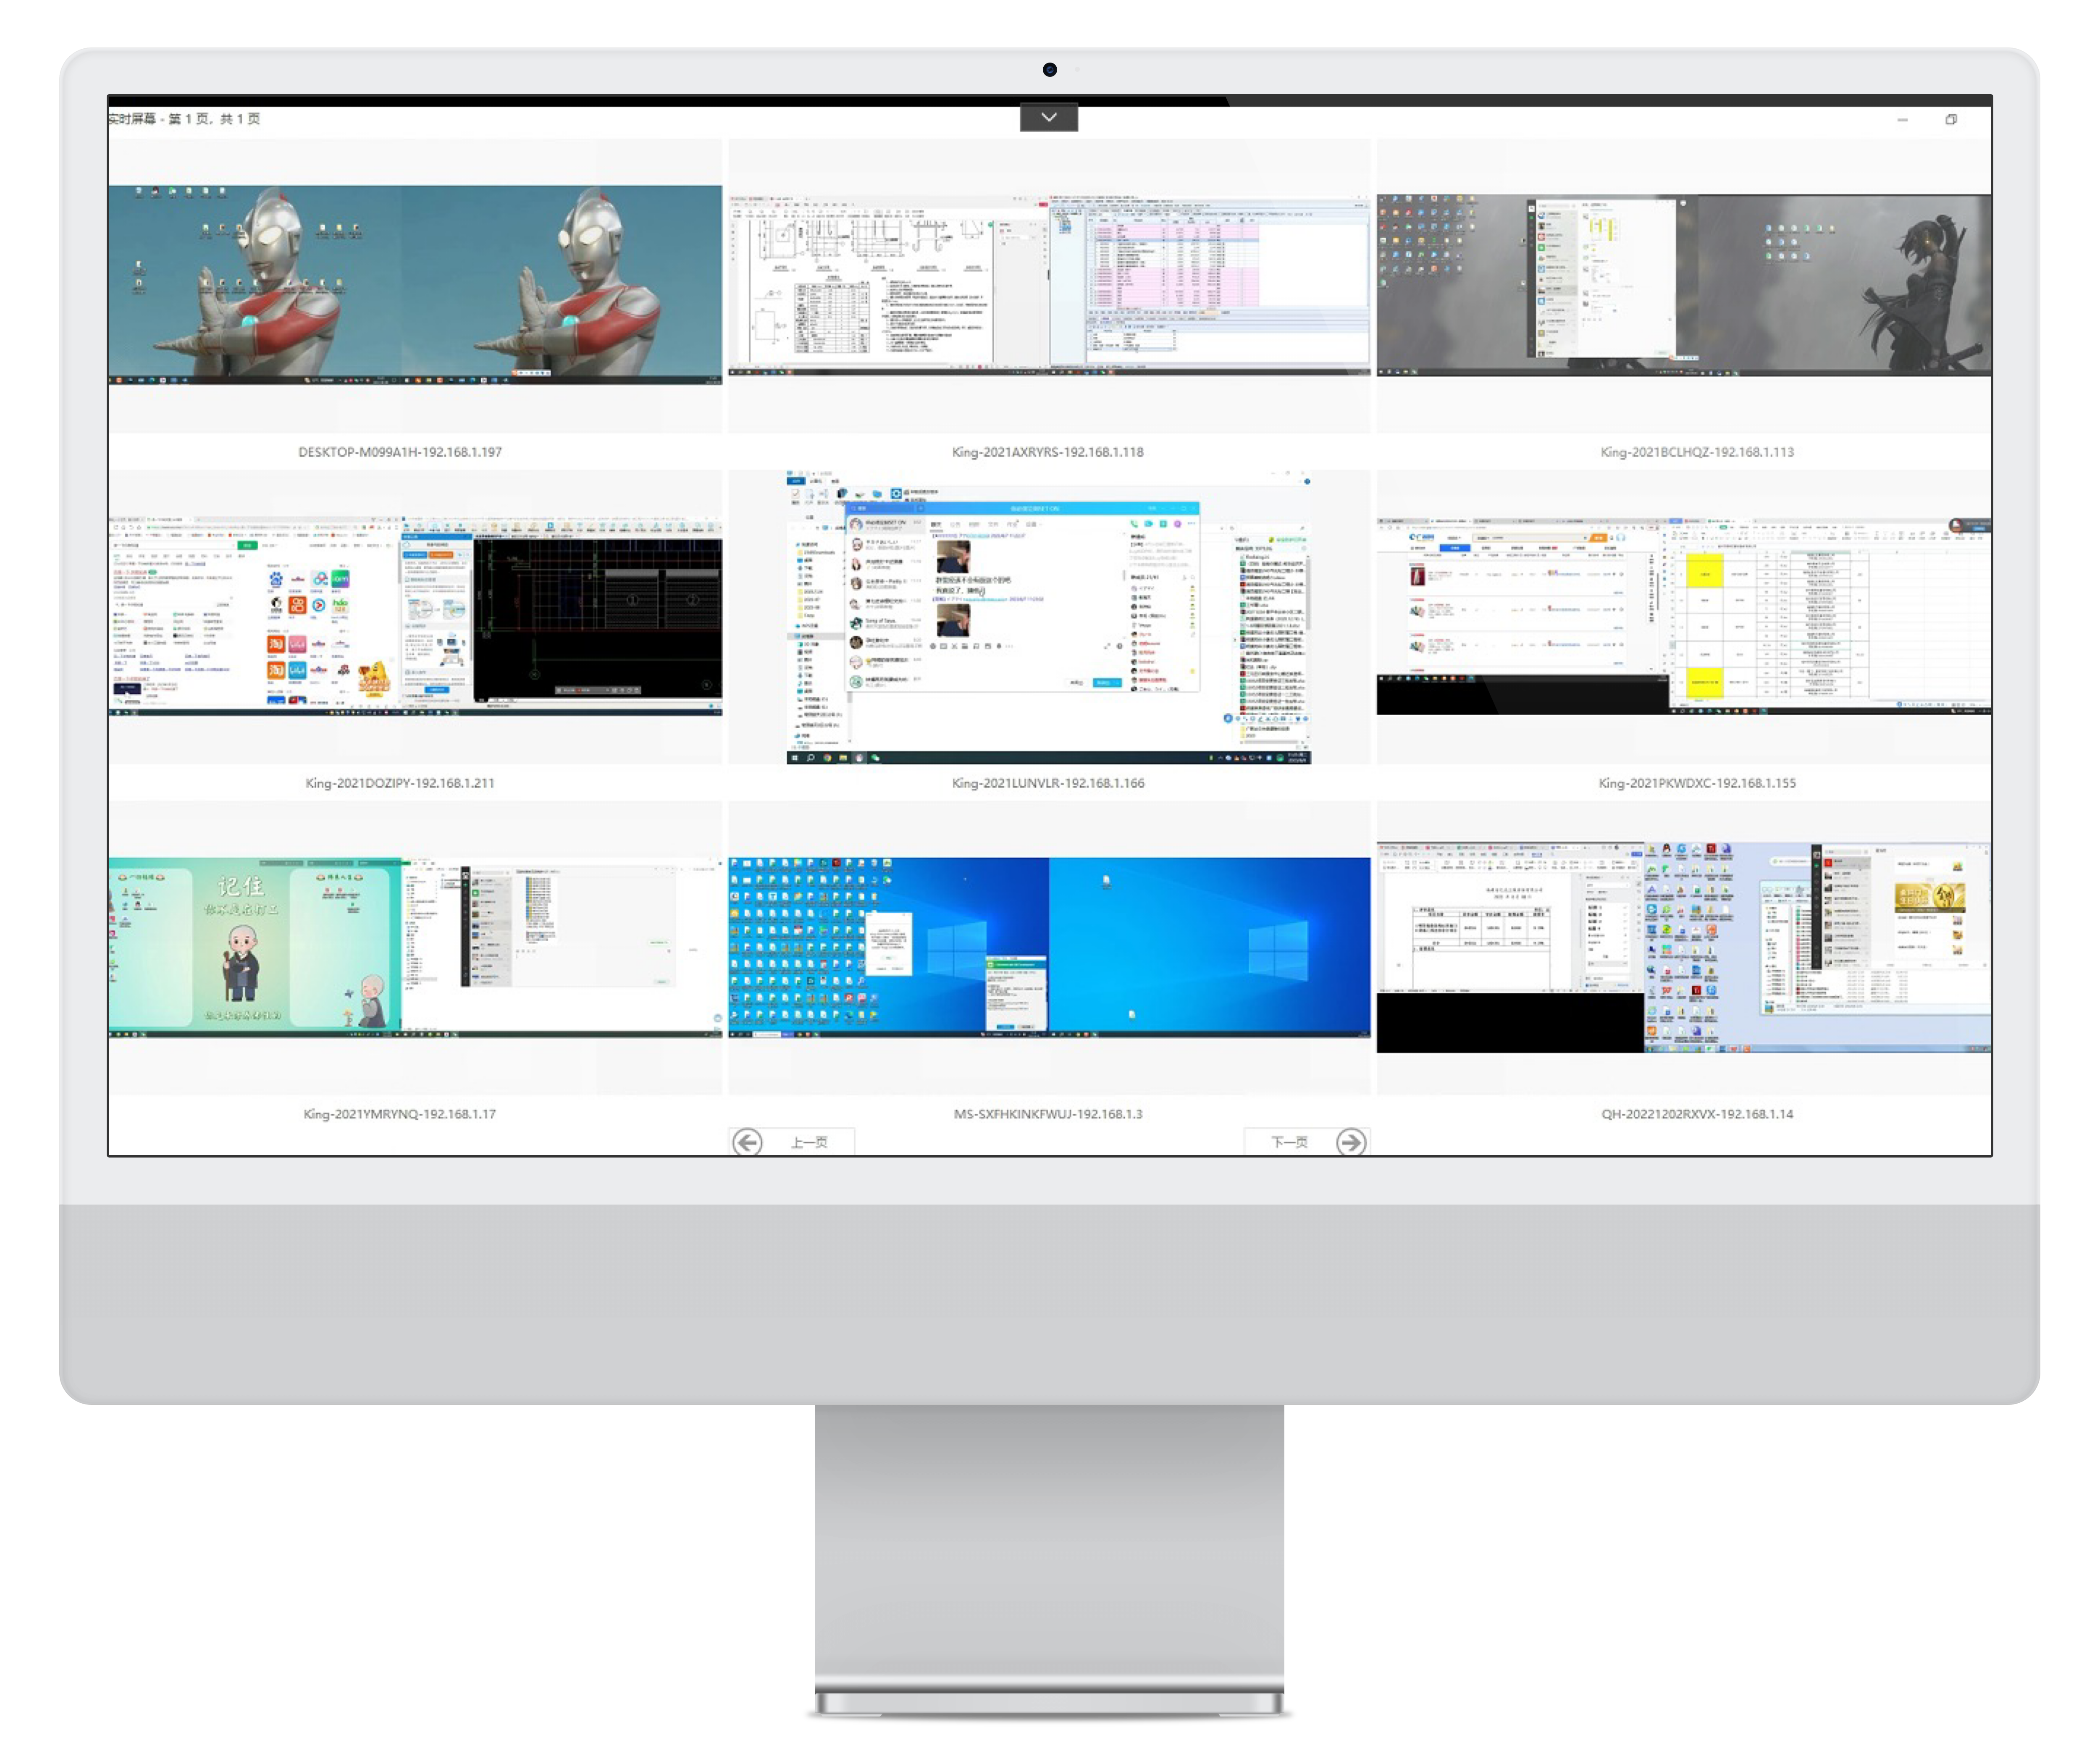 This approach is also called the "thin client" solution. To put it simply, all the code is locked in the server in the computer room, and a monitor is placed in front of the developers. The code can only be entered but not exited. All compilation and debugging are completed on the server side and not implemented locally. This method is extremely effective in preventing leaks at the physical level, but the cost is prohibitively high and it relies heavily on the network. If you cut off the Internet, you will stop working. It is suitable for large financial and military enterprises with deep pockets and who are extremely sensitive to code security. Small and medium-sized enterprises can easily bring themselves down if they play this trick.
3. Code obfuscation and dependency obfuscation
 This is the "hardcore" gameplay of pure technical flow. If it is a compiled language such as Python or Java, the core algorithm is packaged into an encrypted binary module and only the interface is exposed to the outside world. Change the name of the key variable to "IlIl1ll1l", break up the control flow, and invert the logic. Even if the leaker gets the code, he won't be able to read it or run it. This method costs nothing but "hair". It is suitable for protecting the core algorithm library, but if you expect it to prevent the leakage of the entire internal source code, you are digging a hole for yourself - after all, the code itself in the hands of employees is readable.
4. Split sub-modules and permission convergence
 "Divide and rule" passed down from our ancestors. Don't let any engineer get the complete code. Split the core engine, key algorithms, and business logic into N modules and assemble them through APIs or middleware. Back-end pipeline interface, front-end pipeline rendering, algorithm group management model. Even if someone copies the entire code away, it will still be a crippled product when put together. This method has high management costs and requires extremely high architectural design requirements, but once it is established, it will naturally be able to "prevent insiders". It is suitable for products with extremely complex core code logic and clear module boundaries.
Source of this article: Enterprise Data Security Defense Laboratory, XinAn Think Tank
Leading expert: Lao Zhou (Zhou Jianguo)
Editor in charge: Zhao Mingyuan
Last updated: March 23, 2026


 Insight Eye MIT System


 Hebei Public Network Security No. 13019902001038

