
Article summary: In places such as company offices and school computer rooms, the local area network is like an invisible corridor, where files, people, and applications shuttle back and forth. Although it looks closed, it is not absolutely safe: someone conveniently brought in private equipment and brought it with him from an unknown source.
In places such as company offices and school computer rooms, the local area network is like an invisible corridor, where files, people, and applications shuttle back and forth.
Although it looks closed, it is not absolutely safe: someone conveniently brought in private equipment and brought software from unknown sources.; Some people download videos and synchronize network disks for a long time, and the bandwidth seems to be taken away. ; Sensitive information has also been inadvertently released. ……These situations are not uncommon. If we actually encounter them, once the business is stuck, everyone's work rhythm will be completely disrupted.
My personal experience is that if monitoring and management are done well in advance, many things will become small reminders instead of major accidents.
The following six methods are more popular science and more practical. They are not either/or. Combining them as needed will be more practical. The premise is that it is legal and compliant, fully informed and authorized, and supporting systems, employee handbooks, and privacy clauses must be in place together. Only when the process runs smoothly can the system be considered real. “stable".
1. Deploy the Insight MIT system
Applicable experience: The functions are relatively complete, as if it is installed for the network. “Dashboard", making daily inspections less troublesome. After trying it out, I realized that many fine-grained records are very useful when troubleshooting problems.
Abilities probably include:
many Screen View in real time: by screen wall form, exhibit multiple computers of Screen Operation screen。You can clearly see who is modifying the document and who is browsing the web.
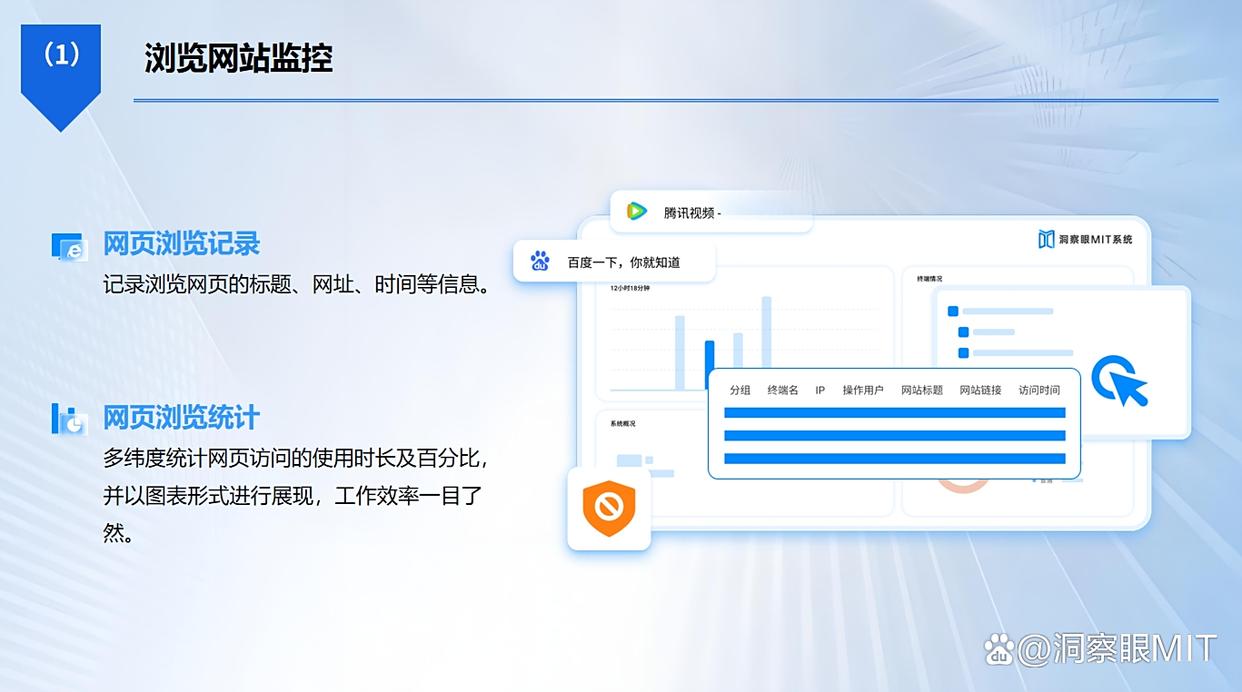
Internet access Behavior Control: Which ones have been visited website、What did you search for? How long to stay,There will be Record and generate a detailed Internet log.
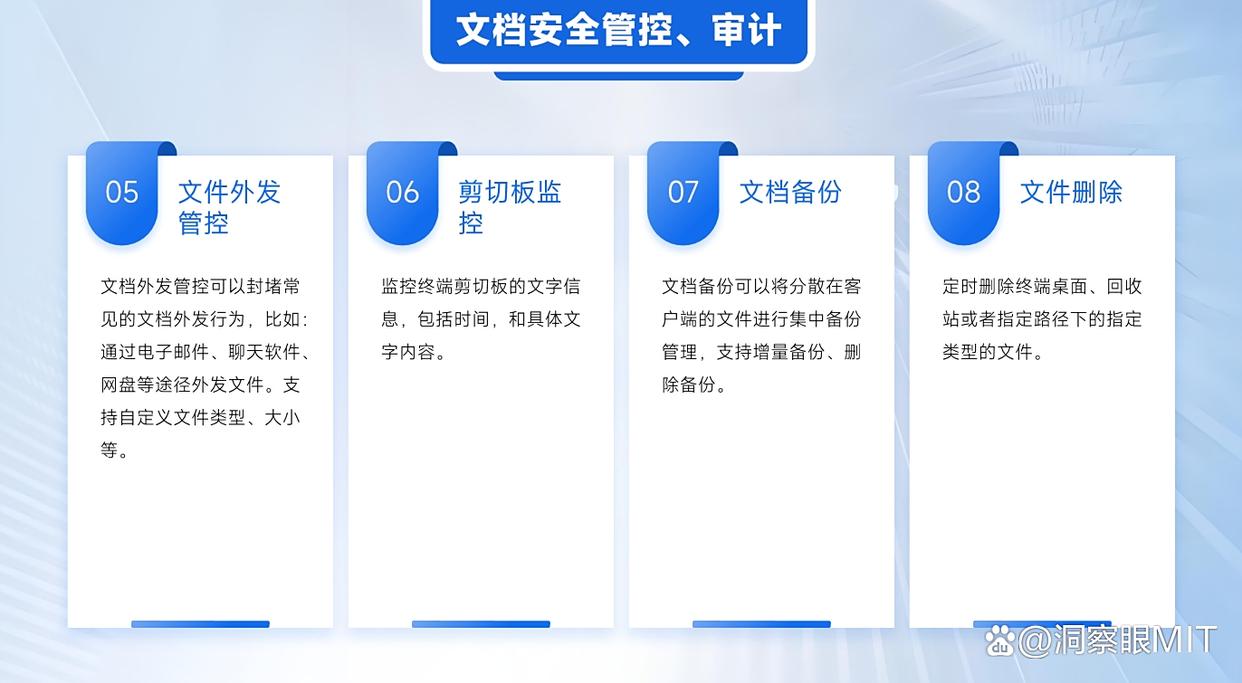
File operation traces: Documentary Creation, editing, deletion, copying, and outgoing are all recorded. include Time, path, operator.
flow monitor :Real-time monitoring Device traffic usage,You can also limit the traffic usage of the device to avoid affecting the progress of key business.
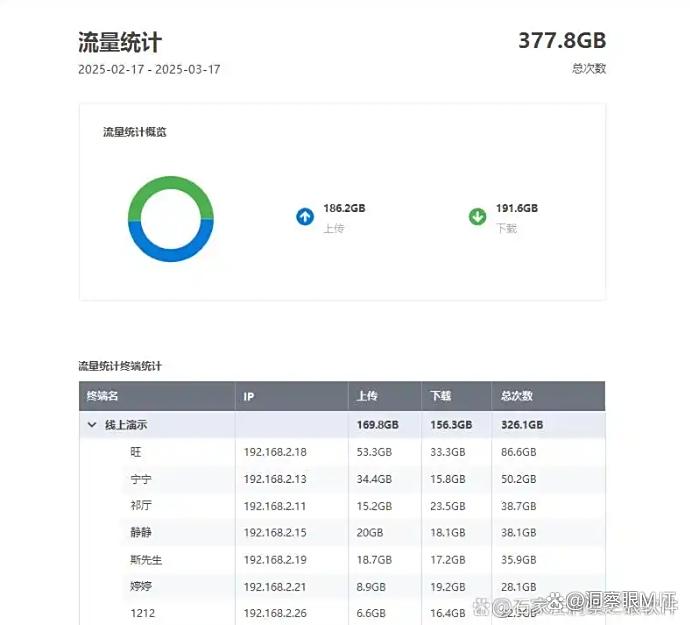
Communication monitoring:For common communication software (WeChat, QQ , Enterprise WeChat) for in-depth monitoring of chat content, including chat time, objects, sent files, etc.
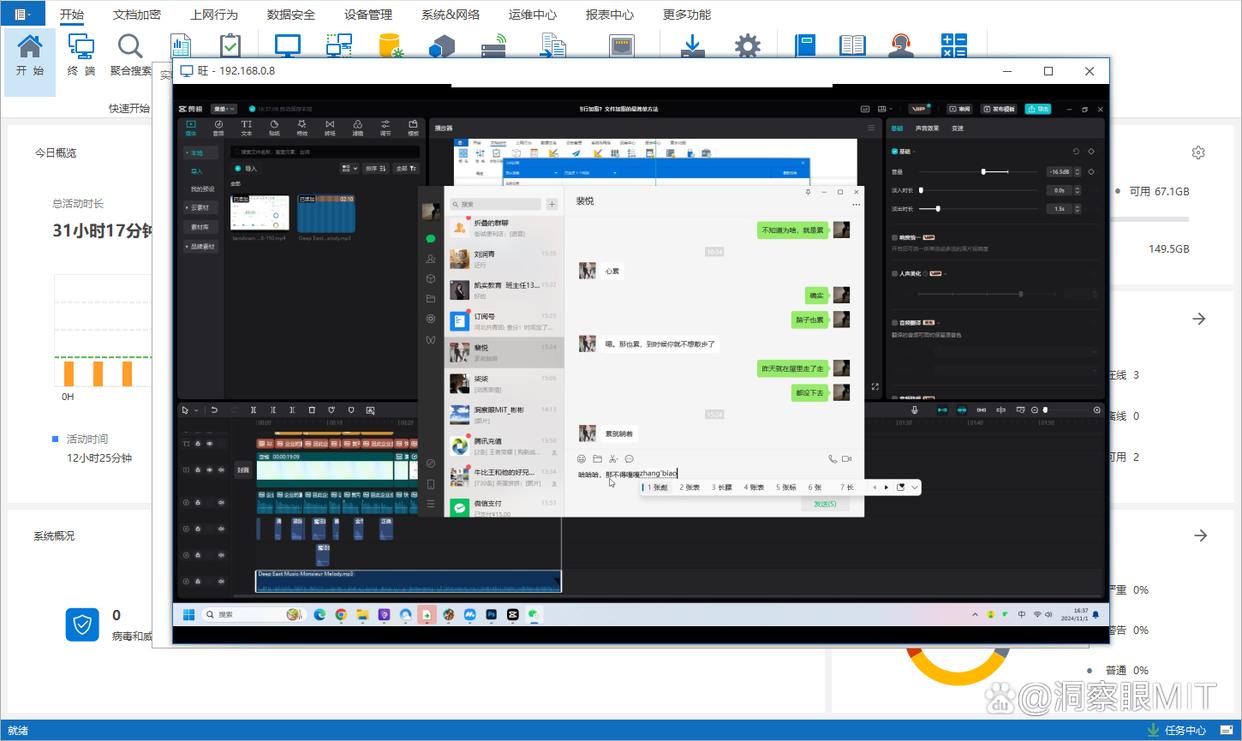
Small scene: There was an evening rush hour when a certain computer sent a large packet to the outside. The bandwidth was directly redlined. The system triggered an early warning. I followed the logs to locate the network disk and synchronized it. It was limited. 10 minutes of bandwidth, the business peak will be stabilized.
2. Better network access control NAC
Simple understanding: If a device wants to access the network, it must first pass an identity and health check. The account password, patch status, and whether the designated security software is installed in place will be released before release. ; Those who fail to pass will be quarantined or have their rights restricted.
Applicable environment: Scenarios with high security requirements such as finance, medical care, and R&D will benefit even more. To the unknown visitor “No", the probability of the virus running rampant will naturally decrease.
Tips: Entry strategy “One size fits all”. It can be layered by role, region, and time, which is rigorous without blocking the business.
3. Enable switch port monitoring
How to do it: Enable port mirroring on the switch, copy the traffic of the designated port to the monitoring port, and use traffic analysis equipment to view protocols, peaks and valleys, and abnormalities.
Applicable value: Troubleshoot network faults and identify traces of attacks such as ARP Spoofing and port scanning are both useful. When the network is interrupted, it is usually faster to capture packets through the mirror port.
Small scene: The fan in the computer room was humming. The engineer was squatting in front of the switch with his coat on. As soon as the mirror port was opened, a short-term packet flood peak immediately appeared. The problem was locked to the upstream port of the switch on a certain floor.
4. Deploy Intrusion Detection IDS
Core points: In-depth analysis of data packets to identify malicious code transmission, abnormal login attempts, lateral movement and other characteristics. Once suspicious behavior is discovered, alert the police immediately and record the source IP , time, method.
Applicable recommendations:Small and medium-sized enterprises are especially worthy of admission because the costs are controllable and the benefits are obvious. Many attacks can be stopped before they cause real damage, making servers and databases more secure.
Replenish: Linked with firewalls and log platforms, alarms can be processed in a closed loop instead of “I saw it, but it was too late”.
5. Use firewall strategies well
Management and control ideas: Set up access control policies at boundaries or within zones. For example, the office network does not directly access sensitive ports of the database, and access to core resources from the external network is minimized and whitelisted.
Observability: Intercepted access will be logged. Long-term analysis can reveal attack trends and whether the strategy should be fine-tuned.
Small reminder: Strategy changes must be made through change orders, and the window period must be carefully selected to avoid blocking normal business by going online.
6. Regularly scan equipment and assets
Daily actions: Use professional scanning tools to inventory all network devices IP、MAC , open ports, operating systems, etc. Comparing with historical records, new additions, changes, and conflicts are clear at a glance.
Applicable scenarios:It is very useful in school computer rooms, multi-floor campuses, and enterprises with a lot of outsourcing equipment. When equipment is in order, faults and vulnerabilities are less likely to be hidden.
Small scene: A new batch of printers was added to a campus. After a scan, the printers whose ports were exposed to improper configurations were immediately marked red. The default passwords were changed, and the security score immediately increased.
Implementation experience
Combination punches are more effective: NAC door, IDS Alarming, firewall isolation, terminal and behavior auditing to fill in the details, combined together, shortcomings will not be easily spotted.
Start small: first select one or two key areas to pilot, run the process and reports smoothly, and then gradually roll out. You will know which strategies will hurt your business only after trying them out, so you need to leave room for adjustments.
People and systems are on the same frequency: monitoring is just a tool, and the supporting permission classification, notification and authorization, data classification, audit traces, emergency response, etc., if any of them are missing, it will easily fall off the chain.
Prioritize compliance: Scenarios involving the audit of employee terminals and communication content must be conducted under the premise of legal compliance. Employees should be informed and authorized, the scope and purpose should be clear, and excessive collection should be avoided.
If these six tricks are used steadily and compliantly, big problems in the local area network can often turn into small fluctuations, and security and efficiency can be improved together. The ultimate goal is not just to install more systems, but to make the network “"Corridor" is cleaner, more controllable, and more able to support business.
Editor: Reiko


 Insight Eye MIT System


 Hebei Public Network Security No. 13019902001038

