
Article summary: Boss, let’s get straight to the point. I know what you fear most. I received a call in the middle of the night saying that the entire core code base had been copied. ; The R&D team suddenly resigned, and the next day a competing product launched a feature that was 80% similar. ; Or worse, not knowing at all
Boss, let’s get straight to the point. I know what you fear most. I received a call in the middle of the night saying that the entire core code base had been copied. ; The R&D team suddenly resigned, and the next day a competing product launched a feature that was 80% similar. ; Or worse, have no idea who, when, or what was leaked. This feeling of "running naked" burns money and even more heartache.
Today I will tell you how to encrypt files, especially our valuable core codes. I will give you 5 methods. The last one is the "treasure" that can really make the boss sleep soundly at night.
To prevent core code leaks, you need to know these 5 tips
1. Deploy the Insight Eye MIT system
Don't get me started on all the bells and whistles. To lock up a company's core assets, you have to use the most hard-core and systematic methods. After working in the industry for so many years, I have made plans for hundreds of technology companies. In the end, the one that was most thoroughly implemented and the boss felt most at ease was to deploy a set of enterprise-level code encryption software like the "Insight Eye MIT System". It does not simply add a password to the file, but builds an "invisible vault" for the entire R&D environment.
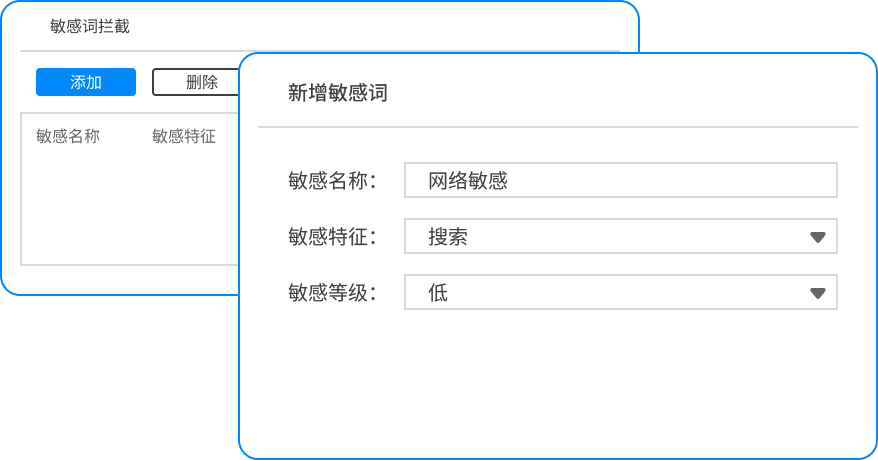
- Transparent encryption, automatic forced landing: Employees cannot sense the encryption process at all. The code pulled down by SVN and Git is automatically encrypted and can be opened locally normally. However, once it is copied without authorization, sent to WeChat, or even copied away with a USB flash drive, the file becomes a bunch of garbled characters. This trick directly cuts off the thoughts of "unintentional mistakes" and "intentional mistakes".
- Fine permissions and strict control of code flow: Who can see the core algorithm module? Who can change the database connection pool? The system can set fine-grained permissions by department, project, or even person. Developers can only see their own piece of code, and architects have global permissions. This minimizes the risk of "one rat droppings ruining the whole pot of porridge".
- Outsourcing control to prevent secondary leakage: The customer wants to see a demo version temporarily? Do partners want to jointly debug an interface? No source files are required. The system comes with a secure outbound function, which generates an encrypted package with time limits, opening times limits, and even binding to the other party's computer hardware. I gave it to you, but you can only use it on the time and machine specified by me. Want to forward it? There are no doors.
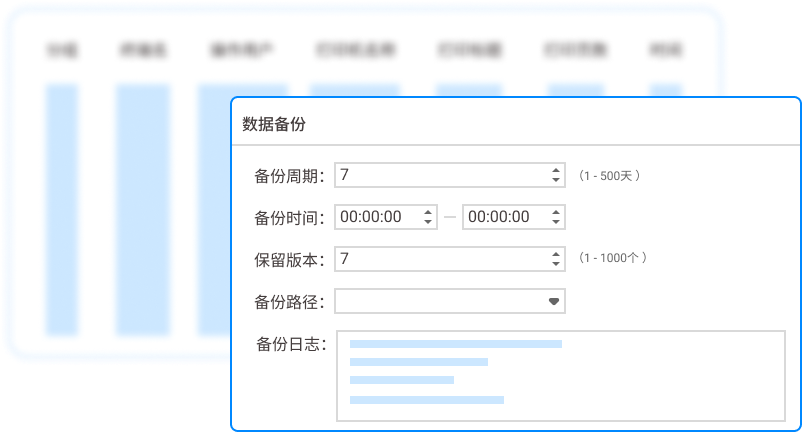
- Log audit, traceability after leakage: If something really happened, we need to know who it was, at what point in time, and which document was touched. The audit log in the background of the system is like a gun. All operations on core files, including opening, modifying, copying, printing, and outsourcing, are all recorded. This is not only a deterrent, but also solid evidence for subsequent accountability and even legal proceedings.
- Offline strategy to plug the last loophole: Don’t think there’s nothing you can do if your employees take their laptops home. The system supports offline policy. After the notebook is disconnected from the Internet, the files are still encrypted. Once the authorization time is up, or abnormal operations are detected, the files are automatically locked and cannot be opened.
2. Use the EFS encryption that comes with Windows
This method is the simplest and most basic. Right-click on the folder, find "Advanced" in Properties, and check "Encrypt content to protect data". The file will be encrypted using your account credentials.
Floor effect : If you develop it alone and use it yourself, that’s enough. But as soon as someone changes people, reinstalls the system, or forgets to back up the certificate, the files "physically disappear" and no one can open them. Disaster for teamwork , the management cost is extremely high, and it is only suitable for small workshops or individual developers.
3. Encrypt the compressed package with password
Set a password when packaging with WinRAR or 7-Zip. Simple and crude.
Floor effect : People who can guard against "one look". But once the password is distributed in the group, it is equivalent to handing out keys all over the street. Moreover, tools for cracking compressed package passwords are now available everywhere, and anyone with a little bit of effort can crack them in a short amount of time. This is not to guard against leaks, but to guard against gentlemen rather than villains.
4. Purchase hardware encryption USB flash drive/server
Spend money to buy a hardware-encrypted USB flash drive with physical buttons, or set up a dedicated encryption machine server.
Floor effect : Physical isolation, security is indeed high. But the problem is that developers have to frequently read and write code every day, plug and unplug U disks, copy to hardware and then decrypt, which is horribly inefficient. This solution is more suitable for top-secret scenarios such as finance and military industry. It is used to protect "static" core claims data. It is not suitable for our code development environment that requires "dynamic" collaboration.
5. Use managed encryption by cloud service providers

Use private warehouses on GitHub, GitLab or domestic code hosting platforms, which usually provide data encryption at rest.
Floor effect : Can prevent external attacks such as "server being dragged to the library". But the biggest risk is "internal": after employees clone the entire code from the cloud to local, they are out of the protection of the platform. It's like installing a good lock outside your warehouse, but if a thief moves the entire warehouse away, you can't do anything.
After working in this industry for so many years, I have seen too many bosses slap their thighs after leaks: "I wish I had spent this much money to install the system." File encryption is never a technical issue, but a management issue and risk awareness issue. The first four methods are either single-point protection or sacrifice efficiency for safety. What is truly suitable for our technology companies and can lock the core code in the "inner loop" without affecting R&D efficiency must be something like the "Insight Eye MIT System" Systematic and proactive defense enterprise-grade encryption solution.
Don't wait until the day the secret is leaked to regret it, you should make arrangements for it today.
Source of this article: Enterprise Information Security Internal Reference, CIO Compliance Alliance
Lead writer: Chen Guodong
Editor in charge: Zhao Min
Last updated: March 27, 2026


 Insight Eye MIT System


 Hebei Public Network Security No. 13019902001038

