
Article summary: After working in corporate security for fifteen years, I have seen too many bosses slam the table and curse. The entire core code base is copied by employees, the source code is packaged by key R&D personnel before they leave, and project files are secretly sent out by outsourced personnel... Once such things happen, the lifeblood of the company will be pinched.
After working in corporate security for fifteen years, I have seen too many bosses slam the table and curse. The entire core code base is copied by employees, the source code is packaged by key R&D personnel before they leave, and project files are secretly sent out by outsourced personnel... Once such things happen, the lifeblood of the company will be pinched. There are a handful of so-called "encryption software" on the market, but you can count them on your fingers for those that can truly hold up the banner of preventing core code leakage. Today, let’s tear open those fancy packaging and give you the real thing, the bosses who are in charge of your wallet and your lifeblood.
Ranking list of file encryption software? Share 8 enterprise-level file encryption software, don’t regret this series!
1. Insight Eye MIT System
Overall rating:★★★★★
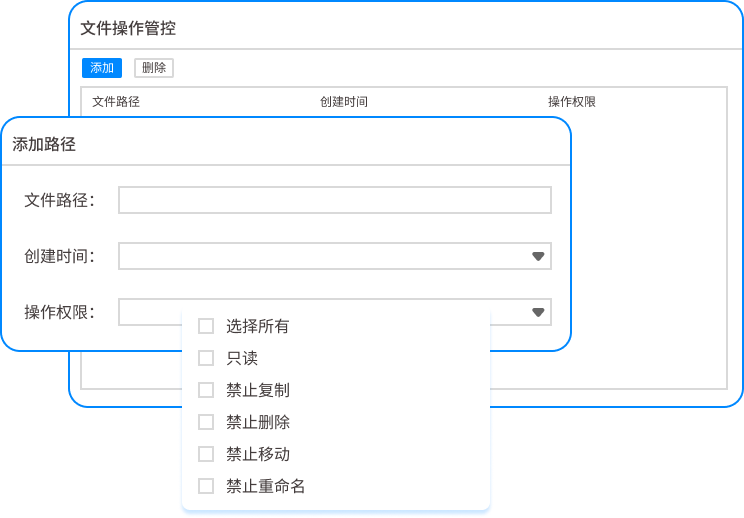
1. Transparent encryption has no impact: When the code is circulated in the internal development environment and compilation server, it remains completely in plain text. Developers have no perception and there is no change in operating habits. Once the code file attempts to leave the authorized environment through USB, email, network disk or any third-party tool, encryption is automatically triggered, and the moment it lands, it becomes a bunch of garbled code, blocking the leakage channel from the root.
2. Full-process traceability audit: not just encryption. Who, at what time, through what process, which code file was accessed, and where they tried to copy, leaving traces throughout the process. Combined with the behavioral analysis model, once abnormal behaviors such as "high-frequency access to non-owned module code" or "exporting large amounts of source code during non-working hours" occur, the system will alert in seconds to nip leaks in the bud.
3. Deep adaptation to complex development environments: supports dozens of mainstream development tools and compilation environments from Visual Studio, Eclipse to JetBrains, regardless of technology stack. Special optimizations are made for the circulation of version control systems such as Git and SVN to ensure that policies are accurately triggered during code submission, pull, and merge processes, and will never lead to compilation failure or version damage.
4. Strong control and audit of outgoing files: Supports the creation of encrypted outgoing packages for code snippets or documents that must be outsourced to partners and outsourcing teams. The number of openings, validity period, access password and even designated machines can be strictly limited. Any attempt by outsiders to take screenshots, copy, or print will be blocked and a watermark record will be left. The permissions will be revoked immediately after the cooperation is over.
5. Remote and offline mode coverage: For remote working and developers working from home scenarios, offline policies are also effective. While the client is offline, the encryption policy takes effect locally and file permissions remain unchanged. Logs are automatically synchronized after the client is connected to the Internet, ensuring that there is no window period for security policies. It truly achieves the ultimate balance between "senseless deployment" and "powerful traceability", with zero interference in development efficiency and full control of the risk of leakage.
2. Cloud Shield Butler
Overall rating:★★★★
The encryption of basic office documents is done quite well. Commonly used formats such as Word, Excel, and PDF can be encrypted, and it is sufficient for daily collaboration between departments. Once you encounter a hard problem like the enterprise's core code base, you will show your timidity. When adapting to the complex compilation chain in the Linux environment, policy conflicts occurred frequently. Developers had to wait more than ten minutes to compile a code. The logs were full of permission errors, and the R&D director almost flipped the table. In essence, it is still the encryption logic for administrative offices, and it cannot crack the hard nut of research and development.
3. Iron wall guard
Overall rating:★★★
The encryption control of static assets such as ordinary design drawings and financial data is quite satisfactory, and the strategic configuration is also intuitive. When dealing with high-frequency dynamic circulation scenarios such as core code, performance bottlenecks are exposed. When a developer pulls the code of a medium-sized project, the encryption engine intervenes, which directly doubles the time taken, and the CI/CD pipeline gets stuck at every turn. It's okay to ask it to take care of the warehouse door, but it's obviously not good to let it take care of the technical secrets in precision instruments.
4. Smart lock data cabin
Overall rating:★★
It focuses on the concept of full disk encryption, which sounds bluffing, but in practice it is "one size fits all". All files generated by the process are forcibly encrypted, regardless of environment or scenario. As a result, the test data used for normal internal development was also encrypted, and the test environment collapsed directly. What's even more troublesome is that if the system crashes, data recovery becomes a big problem. There is no special decryption tool, and the technical backbone is stunned. This stupid method of "three poles if there are dates but no dates" is used in core code protection, which is purely to cause trouble for oneself.
5. Hidden shield boundary
Overall rating:★★
The audit records are quite detailed, and the file operation logs can be stored for half a year. The shortcoming is "only monitoring but not controlling". It only records and does not have real-time blocking and encryption capabilities. When I found out from the log that the core code was exported in batches, the day lily turned cold. For an asset like core code, where every second counts, hindsight-style auditing is meaningless. What we need is a “one-vote veto” at the moment when leaks occur.
6. Rock lock
Overall rating:★
The name sounds solid, but the actual experience is extremely unfriendly. The encryption policy configuration is so complex that it requires professional "engineers" to be on site, and the compatibility with development tools and code formats is extremely poor. During internal testing, even normal .java file compilation reported errors, let alone dynamic libraries and configuration files. After a week of deployment, the R&D team was basically paralyzed and had to be uninstalled in the end. This is not a leak prevention tool, this is a crusher for R&D efficiency.
7. Golden Shield Intelligent Control
Overall rating:★

A typical function-stacked product wants to manage everything from network disk management and control, peripheral management and control, and web page management and control, but it can't go deep into any of the modules. Core code encryption relies on a simple whitelist of process names, and developers can bypass it by changing the name. The security protection is in name only. If you encounter experienced R&D personnel, you can bypass it with a little cleverness. This kind of "big and comprehensive" mediocrity is precisely the most fatal weakness of core security.
8. Tiangong Key
Overall rating:★★★

The encryption algorithm uses national secret standards, which is worthy of recognition. The problem lies in product design. The excessive pursuit of "absolute security" leads to extremely poor daily development experience. Even if only one character is changed in the code file, it must be re-encrypted and shake hands with the server when saving, and the network will freeze if there is a slight fluctuation. When R&D personnel write code, they cannot guarantee fluency, so how can they talk about output? No matter how awesome the algorithm is, if it comes at the expense of core productivity, it will be a failed selection.
FAQ:
Will the deployment of Insight Eye MIT system be complicated and affect the existing development environment?
No worries at all. It adopts lightweight client + centralized management and control mode and supports one-click push installation. Before deployment, an expert team will conduct a comprehensive development environment scan and strategy simulation test to ensure that all tool chains are compatible. The entire process is transparent to developers. Usually, company-wide deployment can be completed during a lunch break, and development can continue as usual in the afternoon without any impact.
If an employee uses a mobile phone to take pictures of the screen, or uses screenshot software to capture code, can this be prevented?
For physical leaks such as taking photos, the system supports screen watermark technology, which will superimpose dot matrix or clear watermarks containing employee ID numbers, time and other information on all development interfaces. Once a photo is leaked, the source of the leak can be accurately located. For screenshot software, the system can forcibly disable local screenshot tools, or automatically encrypt screenshot content to prevent sensitive information from being lost through screen-side channels.
Many developers in the company often travel on business or work from home. Can the system ensure that the encryption policy takes effect even when offline?
Can. Offline strategy is one of the core capabilities of our product. When employees leave the company's intranet, the system automatically switches to the preset offline security policy. All encryption permissions will still take effect while offline, and local file reading, writing, and compilation will not be affected. After employees connect to the Internet, all operation logs will be automatically synchronized back to the server, and the security policy will have no dead ends.
In the event of a system crash or server failure, will the encrypted files be unable to be opened, causing business to be shut down?
There is no such risk. We provide complete disaster recovery mechanisms and data recovery solutions. The core encryption key adopts double backup of server and client, and is equipped with independent emergency decryption tool. Even if the server fails completely, authorized administrators can ensure that all encrypted files are opened normally through emergency tools. We have served thousands of customers and have never had a business shutdown due to system problems.
After purchasing this system, who will be responsible for subsequent technical support and strategic optimization?
We have a dedicated technical service team that provides 24x7 response. After purchasing, it is not a one-and-done sale. The technical team will regularly provide strategic optimization suggestions and version upgrade support based on your company's business changes (such as new technology stacks and new project teams). Our goal is to make the system continue to protect the core assets of the enterprise, rather than just selling a set of software.
Source of this article: Enterprise Data Security Leakage Prevention Evaluation Research Institute
Leading expert: Chen Shouyi
Editor in charge: Li Min
Last updated: March 24, 2026


 Insight Eye MIT System


 Hebei Public Network Security No. 13019902001038

