
Article summary: How to prevent source code leakage more securely? I put together some of the pitfalls I've stepped on and the lessons I've learned, and summarized them into five moves that can be implemented on the same day. Let’s talk about a small scene first. At a regular iteration meeting on a Wednesday afternoon, everyone was doing a review while drinking instant coffee.
How to prevent source code leakage more securely? I put together some of the pitfalls I've stepped on and the lessons I've learned, and summarized them into five moves that can be implemented on the same day.
Let’s talk about a small scene first. During a regular iteration meeting on a Wednesday afternoon, everyone was doing a review while drinking instant coffee. It turned out that the production key was mixed into the test environment. ——No one does it on purpose, but leaks often happen quietly.
External attacks, remote collaboration, internal overreach, temporary outsourcing... there are too many risk points. Rather than waiting for something to happen, it is better to lay down the basic skills. The following five tricks should be operable and avoid detours.
1. Deploy the Insight Eye MIT system
Transparent encryption: Using transparent encryption technology, the storage and transmission of source code are automatically encrypted, making development and use almost invisible.; Automatically decrypted only when authorized for use.
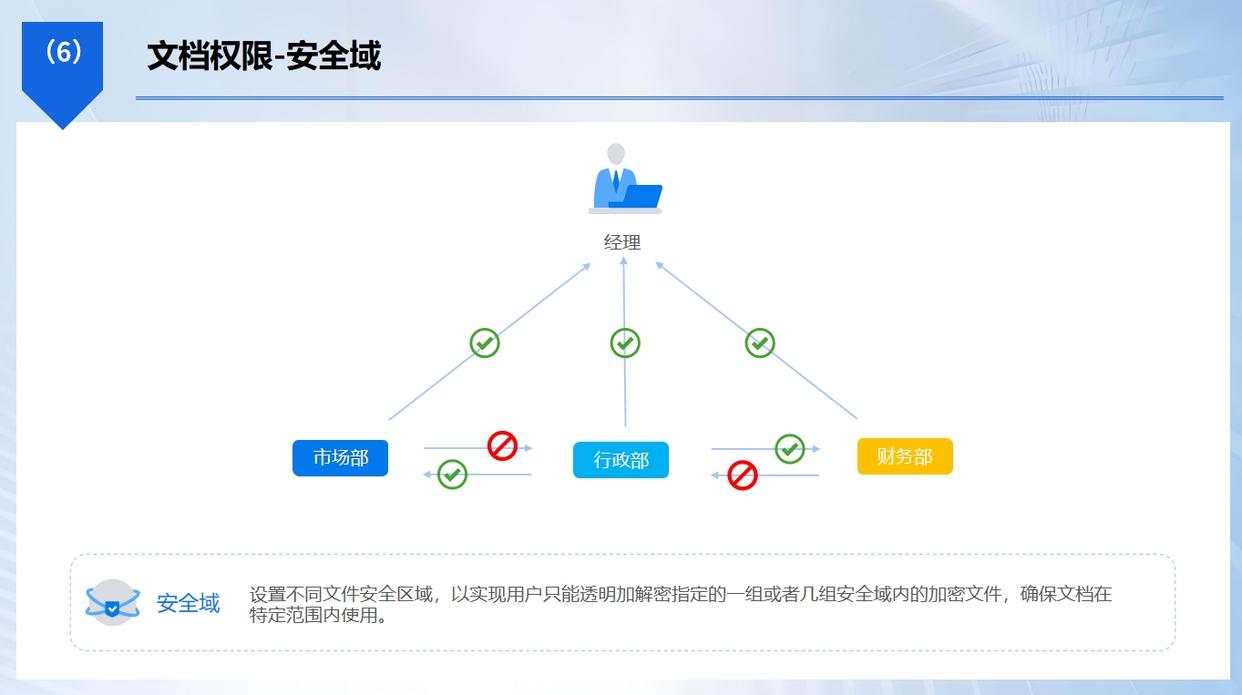
Permission button “"Minimum Sufficient" comes: by organization/project/Role allocation access and operation permissions, denied by default; Restrict high-risk actions such as copying, saving as, and batch exporting ; If necessary, take screenshots, clipboard, U Make strategic restrictions on the inventory, especially for confidential warehouses.
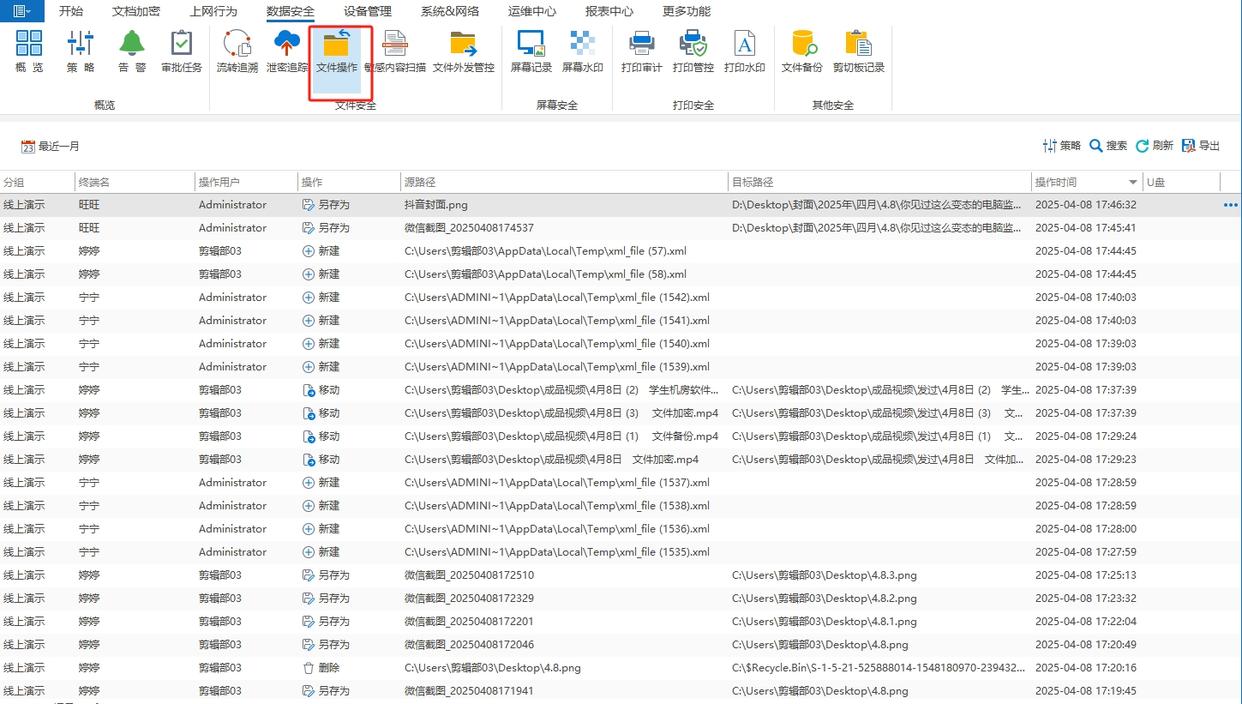
Full-link traceability: all actions such as opening, modifying, downloading, uploading, and sending are recorded by the operator, time, device, and source. IP , and generate logs. Once an exception occurs, the source can be quickly traced through the logs.
outbound Approval : Establish multi-level approval. Before outsourcing, submit an outgoing application. The application should indicate the name of the document, who it is sent to, what its function is, and other key information. It can only be outsourced after the approval of the main person in charge.
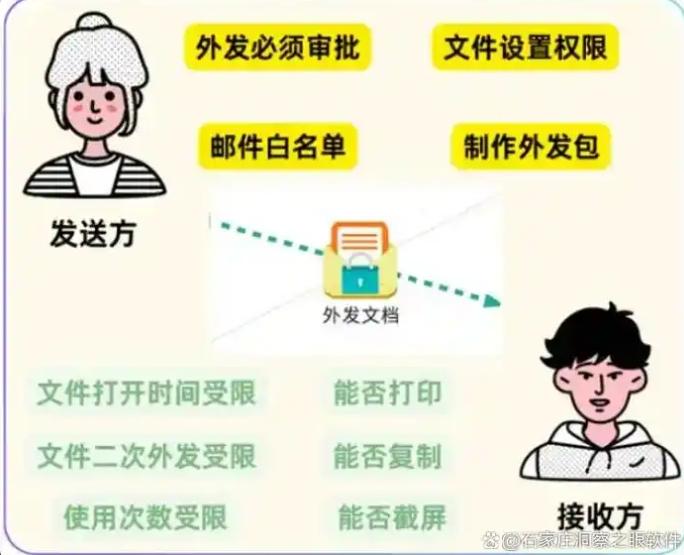
Outbound control: Yes Encrypt outgoing files, also Set the number of opens、Validity period、Device binding, superimposed traceability watermark,Prevent files from being leaked randomly during outgoing distribution.
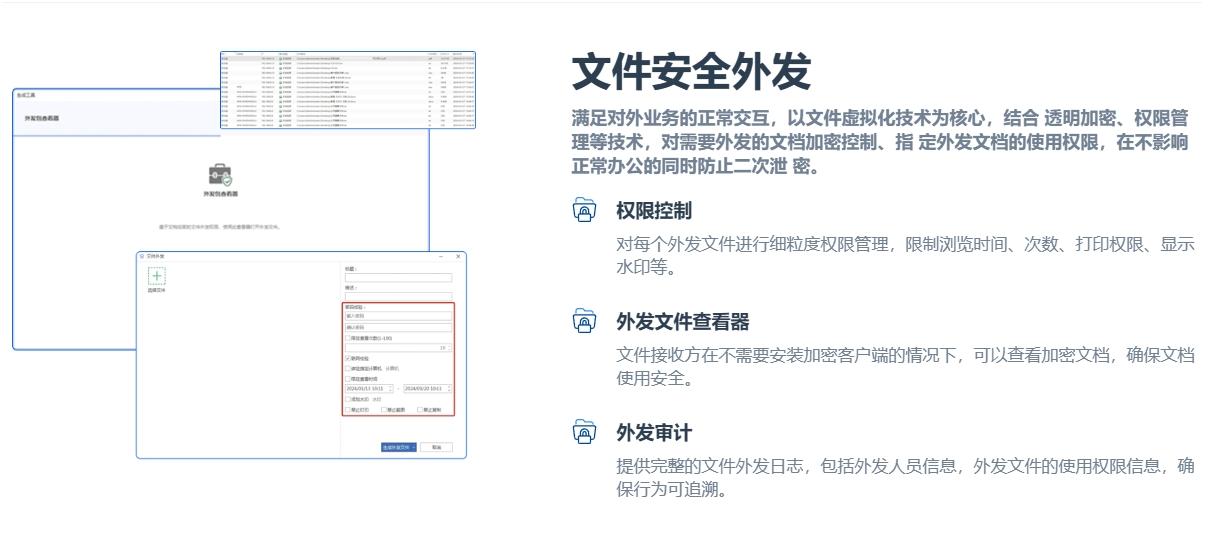
Tips: It is almost normal to send out temporarily on Friday night. Set a clear goal for the person in charge. SLAs (for example30response within minutes), don’t let your business have to choose between tunneling and timeouts.
2. Insert “desensitization and obfuscation” into the assembly line, and it will be safe by default
The core information should be removed first: sensitive content such as algorithm parameters and keys should be desensitized or encrypted and placed in environment variables./Key management service, available on demand at runtime. "Temporary" written to death in the warehouse key ”80% will become a permanent mine.
Increase reverse cost: make variables for front-end and client code/Class name obfuscation, control flow flattening, string encryption, etc. are all appropriate and pay attention to performance regression.; The server can also strengthen key modules to reduce the possibility of malicious analysis.
Execution unattended: Desensitization/obfuscated embedding pre-commit、pre-receive and CI/CD of build Stage, mandatory check before merging; Just open a set SAST/Secret Scanning (like gitleaks/trufflehog ), the key will be blocked if the key is found, and false positives will be whitelisted for management.
Experience feelings: made “After defaulting to "the only way to go", everyone became more relaxed. After trying a small project, they realized that it was not as complicated as they thought.
3. Remote development must have strong constraints: zero trust, managed devices, and cloud hands-on
Identity verification does not go through the motions: Zero trust approach, verification every time you visit; If necessary, add challenges based on risk (location, time, equipment status).
Device compliance before access: Only managed devices are allowed to access core code; Full disk encryption, EDR Normally open, screen saver automatically locked, USB/ Clipboard is controlled by policy. Personal devices either go into containerized workspaces or go VDI/ Cloud desktop; It is strictly prohibited to store code on unencrypted disks.
Only in the cloud: Passed Web IDE , bastion host or remote development agent to the code warehouse, downloading is restricted; Set a threshold for large file transfers. If they are exceeded, they will be blocked or confirmed twice.
Transmission and Monitoring: Mandatory TLS 1.3 Waiting for protocol to transmit data ; Real-time alerts and automatic blocking of behaviors such as unauthorized directory access and large traffic during abnormal periods. By the way, it is very dangerous if the firmware of your home router is not updated for two years. WPA3 Don’t forget to upgrade the firmware.
4. Leak emergency response should have a script: discovery-blocking-evaluation-repair-review
First block Let’s talk about something else: Locate the source through auditing, freeze the account, revoke the token, and revoke immediately SSH Key/Personal Access Token ; If necessary, temporarily close external network access to suspicious warehouses. If hard-coded keys are involved, rotate the keys first.
Quickly assess losses: classify and determine the core extent and scope of the leaked code; Can desensitize /Resolve confusion as soon as possible; Contact the platform for removal /delete( DMCA/Takedown It’s best to have someone familiar with this type of process beforehand). Legal affairs must simultaneously preserve evidence: timelines, submission hashes, logs, packet captures, and screenshots. It is critical that the evidence chain is complete.
Standard procedures and drills: define a set “"Discover - Classify - Respond - Repair - Review" SOP ,clear RACI and address book (security, R&D, legal, PR What do each do?); Tabletop drills are held every quarter, and occasionally night drills are held at two o'clock in the morning. PagerDuty Once you hear it, you will really learn how to collaborate.
Don’t follow the formality of the review: put it “Write clearly why it happened, why it was not discovered earlier, and how to avoid recurrence." and implement it into the configuration./process/Specific changes to tools.
5. Use agreements and systems to get the bottom line: it can be explained clearly, it can be signed, and it can be controlled
Obligations must be clear: employees’ confidentiality obligations during and after employment are written into systems and agreements; The scope of use of the code, the boundaries of external disclosure, and open source compliance must all depend on human opinions. The partner limits the use, scope, and duration, and prohibits leakage and transfer.
There is a basis for pursuing liability: liquidated damages are agreed upon/Loss compensation, evidence collection methods and dispute resolution paths; Enterprises must have a daily spot check and audit mechanism, and when signs are discovered, they can solidify evidence in a timely manner and follow legal procedures (if you delay for one day, the evidence may be reduced by half).
Chain protection is not interrupted: the partner’s subcontractors also sign confidentiality agreements and are included in the audit; A safety assessment will be conducted upon entry, and the media will be returned upon departure. /destroy. Permissions on the day of resignation T+0 Recycling, device verification and data erasure should have checklists to check off.
Little experience: System should not be written as “Long speech hanging on the wall", used for orientation training of new students10I will tell you two real cases every minute, which is much more effective than memorizing clauses.
Editor: Reiko


 Insight Eye MIT System


 Hebei Public Network Security No. 13019902001038

