
Article summary: Boss, let’s open the skylight and speak frankly. The technical team that you spent millions or tens of millions to maintain and stay up late to knock out the core code is the lifeblood of the company. But have you ever thought that this pile of "lifeblood" may be lying naked now?
Boss, let’s open the skylight and speak frankly. The technical team that you spent millions or tens of millions to maintain and stay up late to knock out the core code is the lifeblood of the company. But have you ever thought that this pile of "lifeblood" may now be lying naked on an employee's personal computer or USB flash drive, or even packaged and sent to a competitor's mailbox? I have been working on code leaks for decades and have seen too much. There are all kinds of tricks like frantically copying files on the eve of resignation, sending them out via chat software, or even directly removing the hard drive. Today I won’t talk to you about the nonsense, but will go directly to the practical stuff, how to weld this pile of code to a safe.
How to encrypt source code? These 10 ways to make core code safer than money
1. Deploy the Insight Eye MIT system
 This thing is the most ruthless "watchdog" I have ever seen and the most understanding of the boss's mind. It does not install a lock for you, but turns the entire environment into a safe. Don't listen to the "experts" outside talking about cloud encryption and hardware locks. They are just illusions. The Insight Eye MIT system is real and specializes in treating all kinds of dissatisfaction.
Kernel-level transparent encryption, employees have no idea
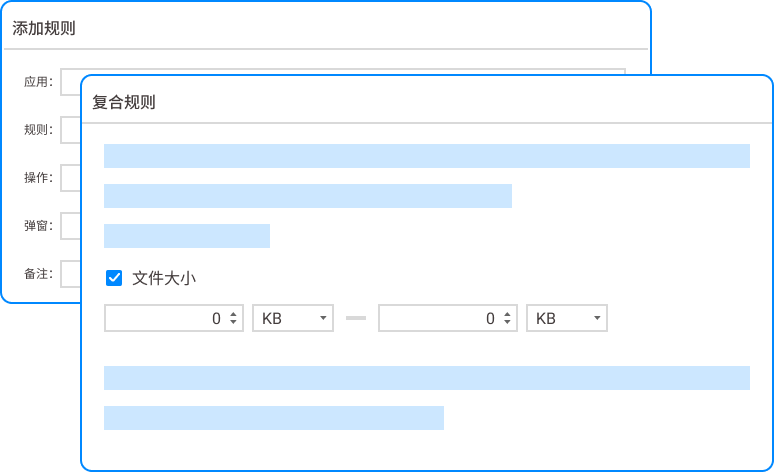
- Implementation effect: Set the policy in the background, and all core codes will automatically complete high-strength encryption as long as they are generated or saved in the specified directory. Employees open Visual Studio and IDEA and type code as usual, and the process remains unchanged. But you want to copy this file to a USB flash drive, send it to WeChat, or upload it to a GitHub private repository? There is no way! It's a bunch of gibberish when it's sent out. We call this "tight inside and loose outside". Employees don't feel that they are being monitored, but all the ways to leak secrets are blocked.
Outbound approval and truncation to block "legal" leaks
- Implementation effect: What should I do if I need to send code snippets or logs to communicate with customers or outsourcing? The system directly manages the outbound process. Employees have to submit an application, stating who it is to be sent to and for what purpose, and the boss or supervisor approves it with just one click on their mobile phone. The files you send out can also be set with an opening password, expiration date, and even prohibition of printing. If you think about it, even if there is a mole who really wants to sell the code, what he will get is a bunch of encryption shells. Who will buy it?
Full life cycle behavioral audit makes "small actions" invisible
- Implementation effect: Don’t wait until something goes wrong before checking monitoring. This system records all operations, including who, at what time, on which computer, which code file was opened, what tool was used, whether you want to take a screenshot, and whether you want to insert a USB flash drive. I have seen a customer. The technical director just had a weird idea and wanted to package the code while working overtime. The system alerted him in real time. The boss came to him for "tea" early the next morning without even a chance to quibble.
Refined management and control of USB flash drives and peripherals, and physical isolation is also ineffective
- Implementation effect: Many leaks are stuck in the USB flash drive. The Insight MIT system directly turns the USB flash drive into a "brick" on the office computer. It can be set to read-only, so you can only store data in it and cannot copy things out. ; Or simply recognize the special encrypted USB flash drive issued by the company. Physical isolation? It's a joke in front of the system.
Remote destruction and offline strategy, you don’t have to worry if your computer is lost
- Implementation effect: Is there really an employee with evil intentions who takes his laptop home and wants to brute force it? The system has an offline policy. Once it is detected that the company has left the company network environment for more than a set time, the computer will automatically lock and the encrypted files will directly self-destruct or become unreadable formats. Even if the hard drive is removed and mounted on another machine, the data will be lost.
2. Code obfuscation and reinforcement tools
 This trick belongs to the "technical flow" and is mainly aimed at compiled code. For languages like .NET and Java, it is easy to decompile and see the source code after compilation. Use obfuscation tools to mix variable names, class names, and control flow into a mess. Even if it is decompiled, it will be a bible and cannot be read. However, this thing cannot prevent the original code from being taken away directly, and can only be regarded as a supplementary method.
3. Hardware encryption lock (software dog)
 Equip the core server with a hardware dongle, and the program must rely on the physical hardware plugged into the server. Without it, the code won't run. The advantage is that the threshold is low, and it prevents those stupid people who directly copy the hard disk image away. But the shortcomings are also obvious. It cannot prevent insiders from directly copying source code files. Moreover, if the dog breaks down and the entire development comes to a halt, boss, you still have to take care of this small piece of hardware.
4. Virtual desktop infrastructure (VDI) and cloud desktop
 Let all R&D personnel connect to the company's internal virtual desktop to work, and the code will not be implemented. What the employees see on the monitor in front of them is just a picture, and the data typed in on the keyboard is all processed on the server. This fundamentally prevents the code from being stored on the personal computer. But the cost is high, the network requirements are strict, and when you encounter network fluctuations, writing code can kill you. Moreover, what you need to be careful of is the "unfashionable method" of taking pictures at the screen and re-photographing with your mobile phone. This method cannot cure it.
5. Dynamic watermark and screen tracking
 Generate visible or invisible watermarks on the IDE interface, including employee ID, IP, and time information. This trick is not for defense, but for "deterrence". Employees know that with just a screenshot or photo, they can locate who did it. Cooperate with the behavioral audit system to catch the insiders one by one. But used alone, it cannot prevent technically savvy people from using scripts to bypass it.
6. Physical isolation and confidential computer room
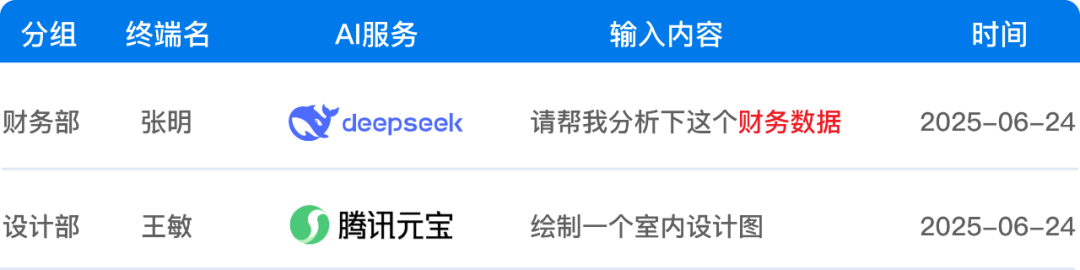 The most primitive, stupidest but most effective method ever. Put the core code library in a closed computer room that has no external network, disables USB interfaces, and does not even allow mobile phones to be brought in. All operations must apply and be accompanied by two persons. This method protects against gentlemen but not villains. The management cost is extremely high and it seriously affects development efficiency. Those still using this trick are basically the core systems of the military industry or banks.
7. Network isolation and DLP data leakage prevention
 Make a fuss at the gateway and switch levels, and use policies to prohibit code files from being sent out of the intranet through HTTP, FTP, email, etc. This is a defensive side that can stop most "foolish" outbound attempts. However, in the face of high-level techniques such as encryption, compression, suffix name change, and segmented transmission, pure network-layer DLP is somewhat inadequate.
8. Strict internal authority management (RBAC)
 Split the code base into modules and assign access rights strictly according to positions and projects. Those who do front-end can only see the front-end code, and those who do back-end can only see the back-end. In this way, if anyone gets a code that they shouldn't read, the system will immediately call the police. But this needs to be coordinated with complete operation and maintenance auditing and process management. If the implementation is not in place, it will be Zhang Kongwen.
9. Regular safety training and employee background checks
 People are always the weakest link in security. Provide regular training on the legal consequences of leaking secrets, and sign confidentiality agreements and non-compete restrictions when joining the company. When recruiting people, do the instep adjustment to keep out those with "criminal records." This trick is to lay the foundation. "Awareness" alone cannot prevent "malice".
10. Code fragment development and key separation
 The core algorithm is split into N code fragments, assigned to different people for development, and finally assembled by a core engine. Store important configuration keys, database passwords, and code logic separately. In doing so, no one has the complete thing in their hands. But this requires the architecture to be designed very cleverly, otherwise you will dig a hole for yourself.
Finally, I want to tell you something from the bottom of my heart: when it comes to code security, don’t think about buying a tool and you can sit back and relax. It is a system, and Insight Eye MIT System In this system, they play the role of the "foundation" and "security captain" at the bottom. It allows you to change from "passive anxiety" to "active control" when it comes to data security.
Source of this article: Enterprise Data Security Alliance, China Information Security Management Research Center
Leading expert: Chen Weidong
Editor in charge: Zhao Min
Last updated: March 27, 2026


 Insight Eye MIT System


 Hebei Public Network Security No. 13019902001038

